Can Employees Using AI Cause a Data Breach?
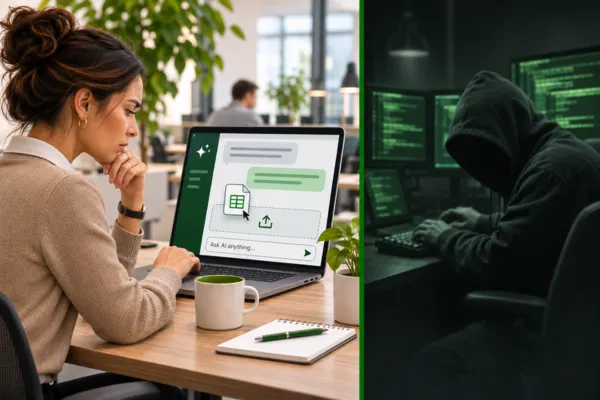
If you’d asked me what comes to mind when I hear the words “data breach,” I would’ve pictured a mysterious man sitting in a dark room wearing a hoodie, hunched over a keyboard and surrounded by computer monitors behind the mayhem. Fast forward to 2026, and that’s not the only way data breaches happen. Today, a breach can start with an employee who’s just trying to finish their work faster. They paste a spreadsheet into an AI tool, use a personal ChatGPT account to summarize information, or let an AI note-taker join a meeting. Most of them never stop to think about where that information goes next.
The short answer: Yes. When staff enter confidential company or client information into AI tools the company hasn’t approved, that information leaves your control. No hacker needed. Hospitals and behavioral health facilities have already had to notify patients after staff used AI tools to finish their work faster, and the same risk applies to any company that handles client contracts, HR files, or financial records.
Key Takeaways
No hacker needed. A data breach can happen the moment an employee enters confidential information into an AI tool the company hasn’t approved.
Shadow AI is likely already happening in your company. Most staff who use AI at work have used it even when they believed it wasn’t allowed.
AI comes in more forms than ChatGPT. Meeting note-takers, browser extensions, personal accounts on phones, and AI features inside tools you already pay for all count.
Small gaps cause big problems. Personal email on a work invite and an incomplete offboarding process led to an AI note-taker leaking information from a patient care meeting.
Banning AI doesn’t stop the problem. A clear policy on approved tools, approved uses, and what data should never be entered does.
What Is Shadow AI?
Shadow AI is the practice of staff using AI tools that the company has never vetted or approved to perform their work. It’s more common than most leaders think. A 2026 PagerDuty survey revealed that 66% of workers who use AI said they’ve used it even though they believed it was against company policy. And IBM’s 2026 Cost of a Data Breach Report reported that incidents involving shadow AI (unauthorized AI use) doubled from 20% to 43% of breached organizations and 68% of companies that had a data breach had no AI policy in place.
Most of the time, staff aren't using AI with the intention of getting their employer in trouble or causing a data breach. Staff use AI because it saves them time, the approved tools don’t do what they need, or no one ever told them what’s allowed. The problem is that a company can’t protect information it doesn’t know is being shared.
Three Real Data Breaches Caused by Staff Using AI:
A spreadsheet uploaded to a public AI tool. In September 2026, an employee at Johns Hopkins Bayview Medical Center in Baltimore uploaded a spreadsheet to a public AI tool the hospital hadn’t approved. It contained details on 3,182 patients, including names, medical record numbers, account numbers, and medications. The hospital had the employee delete the information from the tool, asked the AI company to delete it, and mailed letters to every affected patient with an offer of free credit monitoring.
Case notes summarized in a personal ChatGPT account. At Lake Burien Transitional Care Facility, a Washington state-run facility for youth with intensive mental health needs, a coworker reported that a staff member was using ChatGPT to draft summaries of client case notes. The state found the employee had used a personal ChatGPT account for other patients too. The facility had to inform families that children’s names, diagnoses, and medication information may have been exposed.
An AI note-taker joined a meeting on its own. A doctor resigned from an Ontario hospital in 2023, but no one removed him from the calendar invite list for a recurring patient care meeting. He received the calendar invites via his personal email during his employment with the hospital. Over a year later, he installed an AI note-taking app on his personal device using the same personal email. The app joined his previous employer's patient care meeting on its own, recorded the discussion about seven patients, and emailed a transcript with patient details to 65 people, including staff who no longer worked there.
None of these people set out to cause harm to the companies that employed them. Each breach came from a gap the company didn’t know it had.
Why These Count as Data Breaches
Once information goes into an AI tool your company hasn’t approved, it’s out of your control. You don’t know how long it’s kept, who can see it, or whether the company's data will be used to train the AI. In each case above, the company had to notify patients and ask the AI company to delete the data.
For healthcare and behavioral health providers, sharing protected health information with a vendor that hasn’t signed a business associate agreement (BAA) can itself be a HIPAA violation, and personal AI accounts don’t come with one. Substance use disorder records carry extra protection under 42 CFR Part 2. We cover this in depth in another blog post: Shadow AI and the HIPAA and 42 CFR Part 2 Violation Dilemma.
Other companies have obligations too. Client contracts, nondisclosure agreements, and privacy laws all limit what staff can share. Data breaches like these can lead to class action lawsuits, fines, and other penalties depending on the laws in your state, country, and industry.
Why Banning AI Isn’t the Answer
When leaders hear about breaches like these, the first reaction is often to ban AI. But a ban doesn’t stop staff from using it. It pushes it onto personal phones and personal accounts where you have no visibility at all.
The answer is defining what AI can be used for (if at all), which tools are approved, and what data must never be entered. When staff have approved tools that do what they need, they have less reason to engage in Shadow AI practices.
It’s Not Just a Healthcare Problem
The examples above relate to healthcare, but the same issue happens when staff paste client contracts, proprietary company information, HR files, or financial reports into an AI tool. Many of those cases never come to light.
How to Find Out If Your Staff Are Using AI
Most leaders think they’re just looking for signs of ChatGPT, but AI comes in many forms:
Chatbots like ChatGPT, Claude, and Gemini, on devices they use for work
Meeting note-takers that join calls and send out transcripts
Browser extensions that read or rewrite what’s on the screen
AI apps on personal phones
AI features built into tools you already pay for, like your email, video meeting, or writing software
A few places to start when regulating unauthorized staff AI use:
Ask your staff which AI tools they use, and make it safe for them to answer honestly.
Check your meeting platforms and calendars for note-taker bots.
Review which AI features are turned on in the software you already pay for.
Add AI to your offboarding steps so former staff are immediately removed from meetings, shared files, and connected apps.
Frequently Asked Questions
What is Shadow AI?
Shadow AI is when staff use AI tools their company hasn’t vetted or approved to do their work. It includes, but is not limited chatbots, meeting note-takers, browser extensions, and AI features inside other software.
Can an employee using ChatGPT cause a data breach?
Yes. If an employee enters confidential company data, client, or patient information into an account the company hasn’t approved, that information leaves the company’s control. Whether it must be reported depends on the type of information and the laws that apply to your industry and jurisdiction.
How can an AI note-taker leak confidential information?
Many note-takers connect to a person’s calendar and join meetings automatically. After the meeting, they can send a summary or transcript to everyone on the invite, including people who should no longer be on the invite list.
Should companies ban AI tools?
A ban alone usually pushes AI use out of sight instead of stopping it. A clear AI use policy with approved tools, guidance on how the tools are to be used, and rules on what data must never be entered into an AI platform gives staff a safe way to work.
How do you find out if employees are using AI at work?
Start by asking staff and making it safe for them to answer honestly. Then check meeting platforms for note-taker bots, review AI features in the software you pay for, and update your offboarding steps to ensure former employees are not receiving company notifications.
Find Out What Your Team Has Already Shared
Your staff may already be using AI tools you don’t know about. Our free Shadow AI Cleanup Checklist gives you a starting point and framework to detect staff AI use, find out what’s been entered and where, and establish safeguards to keep it from happening again.
Download the Free Checklist:
https://gemstoneconsultingservices.com/checklist